
The power of a Pentest

built into a portable case
Automated cybersecurity audits, carried out on site in under 90 minutes.
The power of a Pentest
Automated cybersecurity audits,


The Oxyscan Valise
The Oxyscan Valise is an offensive cybersecurity solution: it automates security audits, simulates a pentester’s attacks and detects the vulnerabilities of an infrastructure.
Ready to use, it plugs into the network to be audited and autonomously carries out a complete, accurate and structured audit, with the level of expertise of a penetration test. Designed for auditors, IT service companies and MSPs, it moves from one site to the next, from one client to the next.

Designed and manufactured in France
- 150+
- types of vulnerabilities detected
- < 90 min
- for a complete audit
- 100 %
- local analysis, works offline
- 7
- languages availableFR · EN · ES · DE · IT · CA · PT

Password analysis

Vulnerability scanning

Network mapping

White-label reports

consistent, effective and actionable audits
Consistent
The same method and the same rigour on every engagement: no gaps, no oversights.
Effective
Time-consuming checks are automated, expertise stays focused on analysis.
Actionable
An interactive report in the interface and a complete PDF of about a hundred pages, under your brand.
From reconnaissance to exploitation, the Oxyscan Valise runs a complete pentest autonomously.
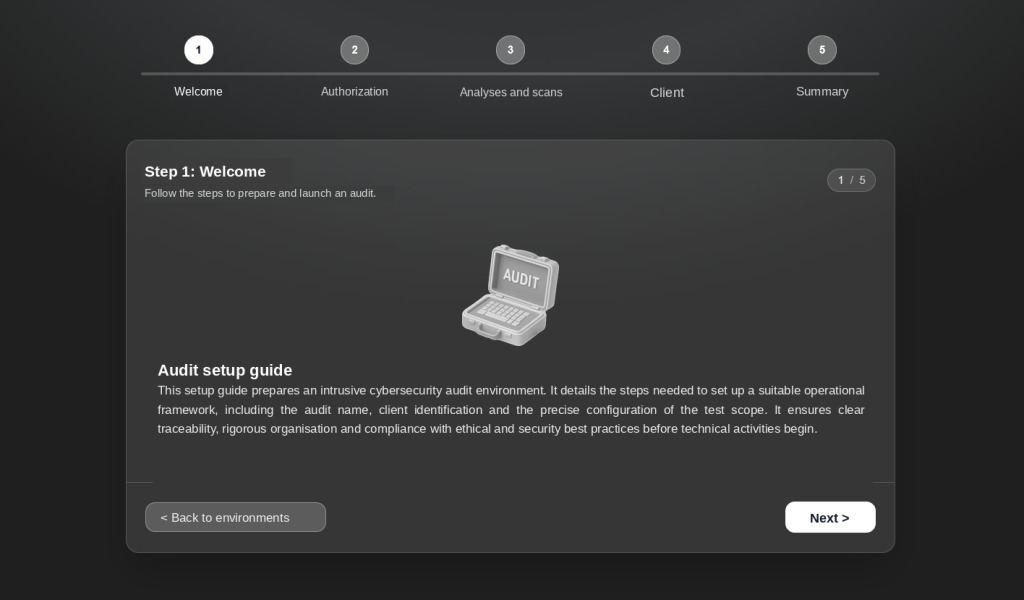
Launch your audits with ease
Launching an audit is guided from start to finish: automatic network detection, structured steps, assisted configuration.
A complete scan starts within a few minutes, fully autonomously, with no particular expertise needed.
Cover your entire attack surface
Internal Audit

Analyse the security of your internal environment: Wi-Fi, Active Directory, web applications, network and critical equipment.
External Audit
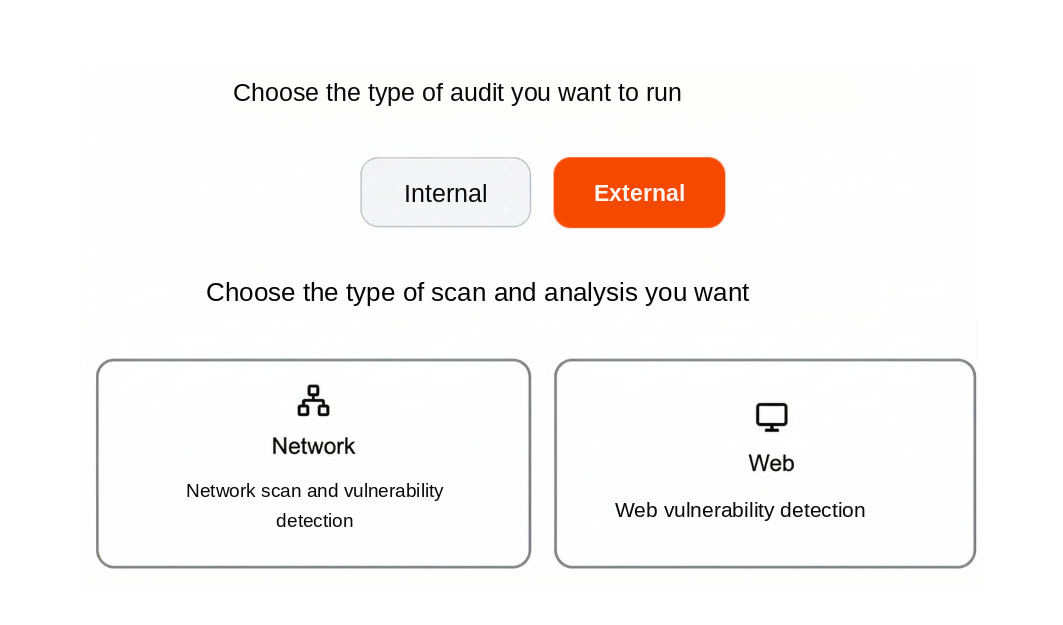
Assess your external attack surface: web applications, accessible services and network components visible from the outside.
Embedded AI, 100% local
An artificial intelligence is built into the Oxyscan Valise and runs on its own hardware: no audit data ever leaves the Valise, even for AI assistance.
100% embedded model
The AI runs on the Valise hardware, with no cloud: usable even on isolated sites, with no data exfiltration.
Contextual detection
Helps detect vulnerabilities that usually require a human eye, and puts results into context.
Report writing
Improves audit report writing, summary and context, directly inside the Valise.
An isolated environment for each client
Built for auditors, IT service companies and MSPs who run back-to-back engagements: every audit starts in a freshly recreated software environment, on a clean dataset.
Isolated by design: no data ever passes from one client to another. Each environment has its own database, its own reports, its own score.
Reactivatable at any time: reopen a past audit for a follow-up visit, extend it or archive it.

Complete audit reports in your own branding
A complete pentest report of over a hundred pages, generated automatically and 100% locally, with no human writing, white-labelled with your branding.

Fix, recheck, prove

Proof of remediation
Every remediated flaw moves from “Vulnerable” to “Fixed”, timestamped in the report.
Recheck in one click
Replay a vulnerability to confirm it has been fixed, without rerunning the full audit.

Score updated live
With every fix, your security score is recalculated immediately.
You stay in control
Ignore or accept a flaw with a comment: a decision that is tracked and reversible.
Connected or 100% offline: you choose
In both modes, analyses, software and data stay entirely on your Valise, inside your network. Connected mode only opens an outbound service channel: it never gives access to your data.
Connected mode
- Automatic updates
- E-mail notifications (Oxydian SMTP relay)
- Automatic certificate renewal
- Set up in 10 minutes
100% offline mode
- No outbound traffic, isolated network
- Updates via offline file
- Suited to air-gapped environments
- Maximum confidentiality
- Same analyses, same reports

Technical specifications
Dimensions: 38.5 × 35.8 × 17.5 cm
Weight: 6.8 kg
Components
- Latest-generation AI chips
- 128 GB of RAM
- High-end components
- 13-inch OLED touchscreen tablet interface
Supplied with
- Power cable
- RJ-45 cable
- USB key (cryptographic validation)
- 2 detachable external Wi-Fi antennas
Why the Oxyscan Valise?
EDR, SOC and antivirus play an essential role, but they do not show where the network is weak: missing updates, shadow IT, obsolete hardware, faulty configurations, weak passwords.
Yet an attacker always goes for the weakest link. Finding it first is the role of the offensive approach, the one behind audits and penetration tests. The Oxyscan Valise puts this approach in auditors’ hands: it automates the techniques of Oxydian’s pentesters to deliver complete, accurate and repeatable audits, directly in the field.
Compare the Valise with traditional solutions
Compare the Valise with
| Criterion | Oxyscan Valise | Manual pentest | Vulnerability scanner |
|---|---|---|---|
| Audit duration | < 90 min | Several weeks | A few hours |
| Expertise required | None | Expert consultant | Analyst |
| Cost per audit | €€€€ out of €€€ | €€€€€€ out of €€€ | €€€€€ out of €€€ |
| Real exploitation of flaws | Yes | Yes | No |
| Ready-to-deliver report | Yes | Yes | No |
| On-demand recheck | Yes | No | Yes |
| Consistency across engagements | Yes | Partial | Yes |
| Works offline, data stays on site | Yes | Yes | Partial |
Relative cost, from € (most affordable) to €€€.
BOX or Valise: which solution is right for you?
The Oxyscan BOX

Continuous monitoring of your network.
- Permanently installed, scans run continuously
- Score and fixes tracked over time
- Automatic executive report every month
- Extensible with multi-site probes
The Oxyscan Valise

The power of a pentest, for one-off audits.
- Powerful hardware, local AI
- Advanced tests: CVE, targeted brute force
- Executive report and full pentest report
- White-label reports
- An isolated environment for each client
- Multi-site and multi-client, built for service providers
The Valise, sector by sector
MSP, healthcare facility, local authority, insurer: the same Valise, different missions.
Frequently asked questions
What is the difference between the Oxyscan Valise and a traditional cybersecurity audit?
A traditional audit ties up a consultant for several days, sometimes several weeks. The Oxyscan Valise automates the same checks on site, in under 90 minutes, and produces the report straight afterwards. The auditor stays in control of the analysis and the presentation of results.
Do you need technical skills to use the Oxyscan Valise?
No. The interface guides each step, from network detection to launching scans: an audit can be carried out without penetration testing expertise. Qualified auditors, for their part, free up time for the most technical tasks.
Does the Oxyscan Valise send data off site?
No. Analyses, password cracking, AI and report generation run on the Valise’s hardware. In connected mode, only an outbound service channel is open (updates, notifications): it never gives access to audit data.
What types of results or reports does the Oxyscan Valise provide?
Two levels of reporting. An interactive report in the interface makes it possible to navigate the findings and prioritise fixes. A complete PDF report of around a hundred pages is generated automatically, along with an executive report for management.
Can the reports be white-labelled?
Yes. Colour, header, first and last page: the reports carry the branding of the provider running the audit.
How long does an audit take with the Oxyscan Valise?
A full audit cycle completes in under 90 minutes, often around an hour. The duration varies with the size of the network and the modules enabled, and advanced tests (CVE checks, targeted brute force) can extend it. Progress is shown live, with the estimated time remaining.
Does the Valise carry out both internal and external audits?
Yes. The internal audit covers Wi-Fi, Active Directory, web applications, the network and critical equipment. The external audit assesses what is visible from the Internet: web applications, accessible services and network components.
Does the Oxyscan Valise work without an Internet connection?
Yes, the Valise can operate entirely offline. Analyses, password cracking and report generation run locally on the on-board hardware, and no data leaves the audited site.
How is my clients' data kept separate?
Each engagement runs in a dedicated environment: the Valise restarts its services on a storage space specific to that client. No data ever crosses the boundary between two environments, and an archived environment can be reactivated at any time for a follow-up visit.
What is the difference between the Valise and the Oxyscan BOX?
The Valise is portable: it is used for one-off audits, across several sites or for several clients. The Oxyscan BOX stays plugged into a network and monitors it continuously.
Book a 30-minute demonstration
Enjoy a personalised demonstration to discover how the Oxyscan Valise automates your on-site audits and pentests, while giving you a clear, structured and actionable view of your infrastructure’s security level. Together, we will look at your challenges and at how our solution can adapt to them.
In just 30 minutes, explore its interface and key features alongside one of our experts, and discover the results, the deliverables and the built-in analysis and reporting capabilities.
