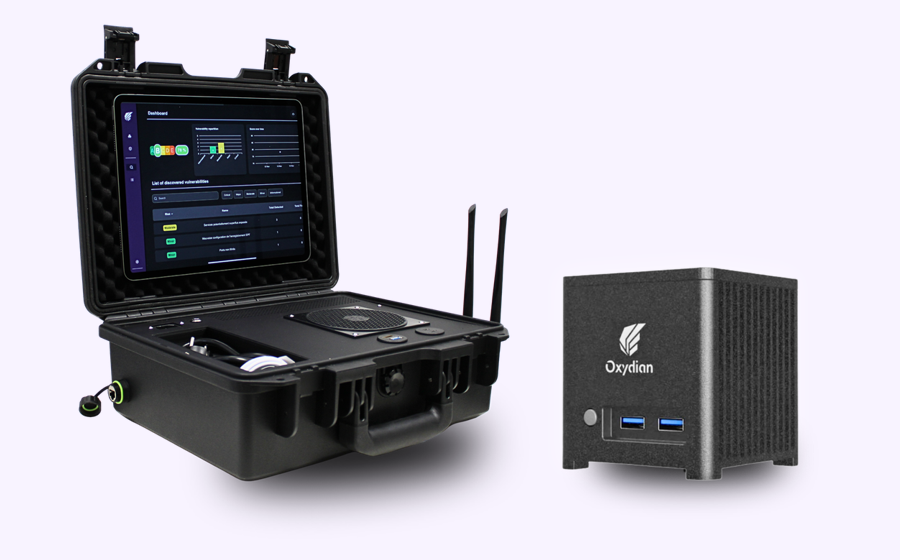
A SOC knows how to monitor and respond to incidents, but its value remains hard to see as long as no attack occurs. The end client's vulnerabilities, meanwhile, often fall outside its scope.
The SOC masters monitoring and response. With the BOX, it can also offer vulnerability detection and management, network mapping and decoys that complement its alerts. A packaged VOC, installed on site, ready to add to the offering.
Decoys that feed the SIEMThe BOX exposes fake vulnerable services, with probes for remote sites, and detects internal attacks: Responder, CVEs, rogue DHCP, scans. Each interaction is sent by webhook to the SIEM or SOAR, with no false positives.
Blind spots revealedPrinters, IoT, network equipment, forgotten servers, off-domain workstations: everything connected is mapped, scanned and monitored every week, including what sends nothing to the SIEM.
Vulnerability management as wellTruly exploitable vulnerabilities, Active Directory, passwords, every week, with the fix explained in the interface. The SOC becomes proactive, with no VOC team to recruit.
Value visible every monthA monthly report in the SOC's branding, readable by management: the client sees the value of their subscription before any incident. Each fix becomes a service to propose.
SOC alone or SOC + VOC
SOC aloneSOC + Oxyscan VOC
Value seen by the clientOn the day of the incidentEvery month, in a report in the SOC's branding
PostureReactive, responding to the alertProactive, fixing before the alert
VulnerabilitiesKnown after the annual audit or after the incidentIdentified every week, fixed as they arise
ScopeWhat has an agent or sends logsEverything with an IP address
One-off
The Oxyscan Valise, a pentester in a case
Plugged into the client's network, the Valise carries out a full audit, internal or external, in 90 minutes on average, with no pentester needed. Where the BOX monitors continuously, the Valise steps in when it matters.
Before signing a new clientAn assessment of an unknown network: mapping, vulnerabilities, Active Directory, passwords, Wi-Fi, internet exposure. The contract starts from a known baseline, with fixes to propose from the very first month.
After an incidentA snapshot of the compromised network: obsolete machines, open services, weak passwords, paths still exploitable. Containment is prioritised on facts and the starting state is documented.
An auditor for back-upThe key supplied with the Valise opens a secure tunnel on demand: for an extra token, an Oxydian auditor takes over remotely to investigate a finding or support an incident response.
An audit in the SOC's brandingManagement summary, findings by criticality, recommendations, screenshots: the report is generated on site and delivered by the SOC team. Annual audit, post-migration check, insurer requirement.
BOX and Valise, the full cycle
BeforeThe Valise sets the initial state and opens the monitoring that follows.
DuringThe BOX monitors every week, alerts the SOC and produces the monthly report.
At the key momentIncident, migration, new site: the Valise comes back to take stock.
Prevention, monitoring and audit with the same team, and a client who sees the SOC's value all year round.
A model designed for SOCs and MSSPs
Partner model
Licence per BOX, a partner discount that grows with the number of active BOXes.
Valise purchased once, then audit tokens individually or in packs: one token, one audit, billed at the partner's rate.
Co-branding, BOX and Valise reports in the SOC's branding.
Onboarding included, analyst training, demo environment, updates and direct support from Oxydian auditors.
Integration
Partner console, the status of every BOX, plus each client's scores and reports, in one place.
Webhook and API, decoy alerts and detections pushed to the SIEM or SOAR, ready for a playbook; vulnerabilities and reports retrievable via API.
Access granted by the end client, a USB key plugged in on the client side gives the SOC full access to the results.
Data stays on site, 100% local analysis, air-gapped installation possible, Valise data kept on removable media.
DownloadThe SOC & MSSP offering as a PDF
Both data sheets, Oxyscan BOX and Oxyscan Valise: key benefits, SIEM or SOAR integration, partner model.